TL;DR: Ransomware protection products block, detect and contain techniques such as LOLBin abuse, credential theft and lateral movement. Best for Deny by Default prevention: Airlock Digital; behavioral EDR with rollback: SentinelOne Singularity Endpoint; managed threat hunting: CrowdStrike Falcon; Microsoft-centric estates: Microsoft Defender for Endpoint.
Leading ransomware protection products use artificial intelligence, behavioral analytics, and storage-layer inspection to defend against advanced and evolving attack techniques. Unlike basic antivirus software, they focus on attacker behavior such as credential theft, privilege escalation, lateral movement, backup tampering, and large-scale file encryption.
Products built for advanced attack techniques typically combine endpoint detection and response, behavioral analytics, application controls, threat intelligence, and automated isolation. They monitor process activity, file changes, scripts, network connections, and authentication events to identify attack chains that may not rely on known malware signatures.
Advanced ransomware attack techniques include:
This is part of a series of articles about ransomware attack.
In this article:
The table below summarizes the key differences between the products covered in this guide. We explore each of them in more detail in the sections that follow.
| Category | Solution | Best For | Key Strengths | Things to Consider |
|---|---|---|---|---|
| Application Control and Allowlisting Products | Airlock Digital | Deny by Default application control across IT, OT and legacy systems | Granular allowlisting, LOLBin blocklisting, VirusTotal intelligence | Policy upkeep where apps update often; frequent agent releases |
| Application Control and Allowlisting Products | ThreatLocker | Zero Trust endpoint platform combining allowlisting and Ringfencing | Ringfencing app containment, dynamic ACLs, device isolation | Steep learning curve; app updates need re-approval |
| Application Control and Allowlisting Products | Carbon Black App Control | Locking down servers, fixed-function and EOL systems | Positive security model with FIM, memory and registry protection | Allowlist upkeep at scale; vendor engagement since acquisition |
| Endpoint Detection and Response Platforms | CrowdStrike Falcon Endpoint Security | AI-native EPP and EDR with managed threat hunting | Indicators of attack, single lightweight sensor, OverWatch hunting | Modular licensing costs; console and query learning curve |
| Endpoint Detection and Response Platforms | SentinelOne Singularity Endpoint | Autonomous EPP and EDR with 1-click ransomware rollback | On-agent behavioral AI, Storyline correlation, rollback | Exclusion tuning at scale; query and console learning curve |
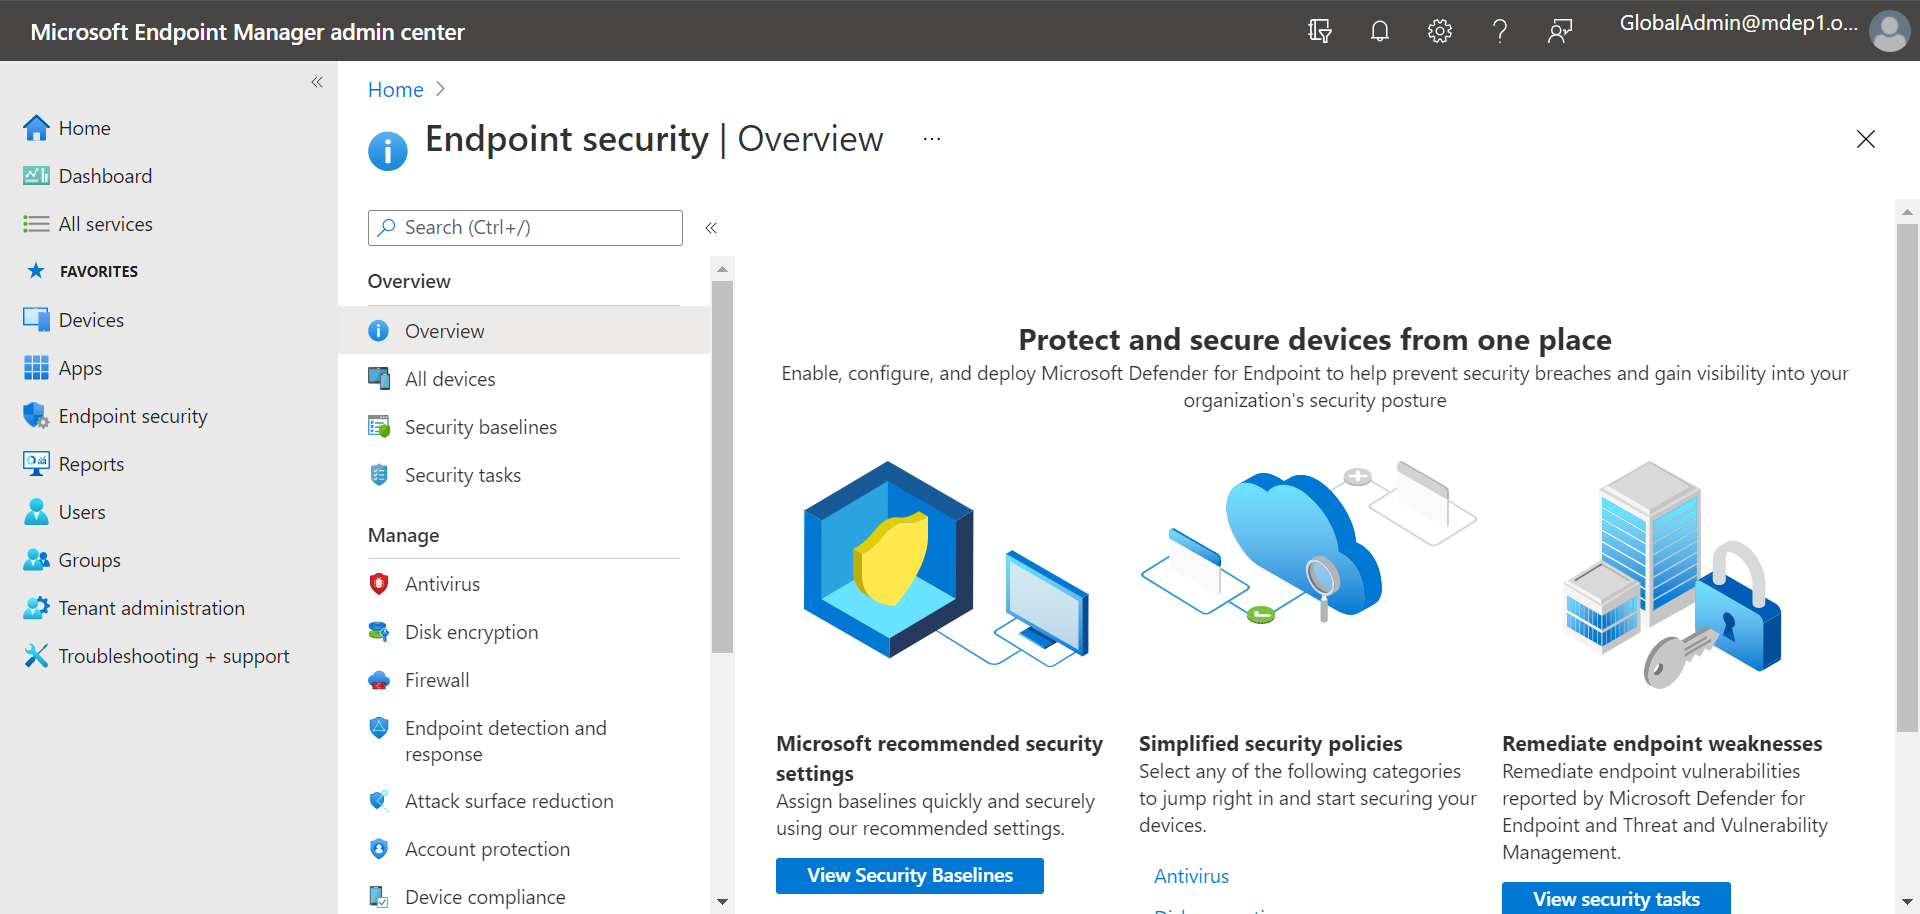
| Endpoint Detection and Response Platforms | Microsoft Defender for Endpoint | Multiplatform EDR integrated with the Microsoft security stack | Automatic attack disruption, global threat intel, Defender XDR | Multiple portals; complex licensing; non-Windows parity |
| Endpoint Detection and Response Platforms | Sophos Endpoint | Prevention-first endpoint protection with default-on mitigations | CryptoGuard rollback, 60+ exploit mitigations, Adaptive Attack Protection | Resource use during scans; console navigation and reporting |
| Endpoint Detection and Response Platforms | Cortex XDR | XDR combining endpoint, network, cloud and identity data | Technique-based prevention modules, root-cause analysis, AgentiX | Learning curve for console and XQL; licensing complexity |
Ransomware operators often use PowerShell, Windows Script Host, JavaScript, or batch files to download payloads, execute commands, and modify system settings. These interpreters are already available on many systems, allowing attackers to perform malicious actions without introducing an obvious executable.
Protection products should:
They should also identify abnormal execution chains, such as an Office application or browser unexpectedly launching PowerShell. Behavioral analysis is important because administrators also use scripting tools for legitimate automation.
Living off the Land attacks use legitimate system binaries, or LOLBins, for malicious operations. Tools such as rundll32, regsvr32, certutil, and mshta can execute code, retrieve files, or interact with system components. Because these programs are trusted and commonly present, their execution alone is not a reliable indicator of compromise.
Detection should focus on how these binaries are invoked, including:
Products should correlate multiple behaviors rather than blocking LOLBins outright. This helps distinguish administrative activity from attempts to download ransomware, execute malicious libraries, or bypass application controls.
Fileless malware executes primarily in memory instead of installing a conventional executable on disk. Attackers may load malicious code through PowerShell, scripts, macros, registry entries, Windows Management Instrumentation, or process injection. This approach reduces the number of files that traditional antivirus scanners can inspect.
Effective protection requires memory and behavioral monitoring that can identify suspicious execution even when there is no malware file available for signature scanning. Products can monitor:
Process ancestry and command-line telemetry can also help reconstruct how the fileless attack began.
Credential dumping extracts passwords, password hashes, tokens, or other authentication material from compromised systems. Attackers can target LSASS memory, the Security Account Manager database, cached credentials, browser data, or other locations containing reusable authentication information.
Ransomware protection products should detect:
Detection should extend beyond specific tools because attackers can modify existing utilities or implement the same techniques in custom code. Correlating credential access with subsequent logins can also reveal when stolen credentials are being used for lateral movement.
Attackers may exploit vulnerabilities, weak permissions, stolen administrator credentials, or misconfigured services to obtain higher privileges. Elevated access can allow ransomware operators to:
Detection should identify unexpected privilege changes, suspicious service creation, token manipulation, exploitation behavior, and processes that suddenly gain elevated permissions. Products should also establish normal patterns for administrative activity so unusual elevation attempts stand out. Monitoring the events before and after privilege escalation helps determine whether elevated access is part of a larger ransomware attack chain.
Remote Desktop Protocol and administrative services provide attackers with ways to control compromised systems and execute ransomware remotely. Valid credentials can make this activity appear similar to normal administration, especially when attackers use built-in remote-management capabilities.
Protection products should detect:
Context such as login time, source device, account privileges, and subsequent process execution can improve detection. Monitoring exposed remote services can also reveal attempts to gain initial access before ransomware is deployed.
After compromising one system, ransomware operators often move through the network to reach servers, domain infrastructure, backup systems, and additional endpoints. Common mechanisms include:
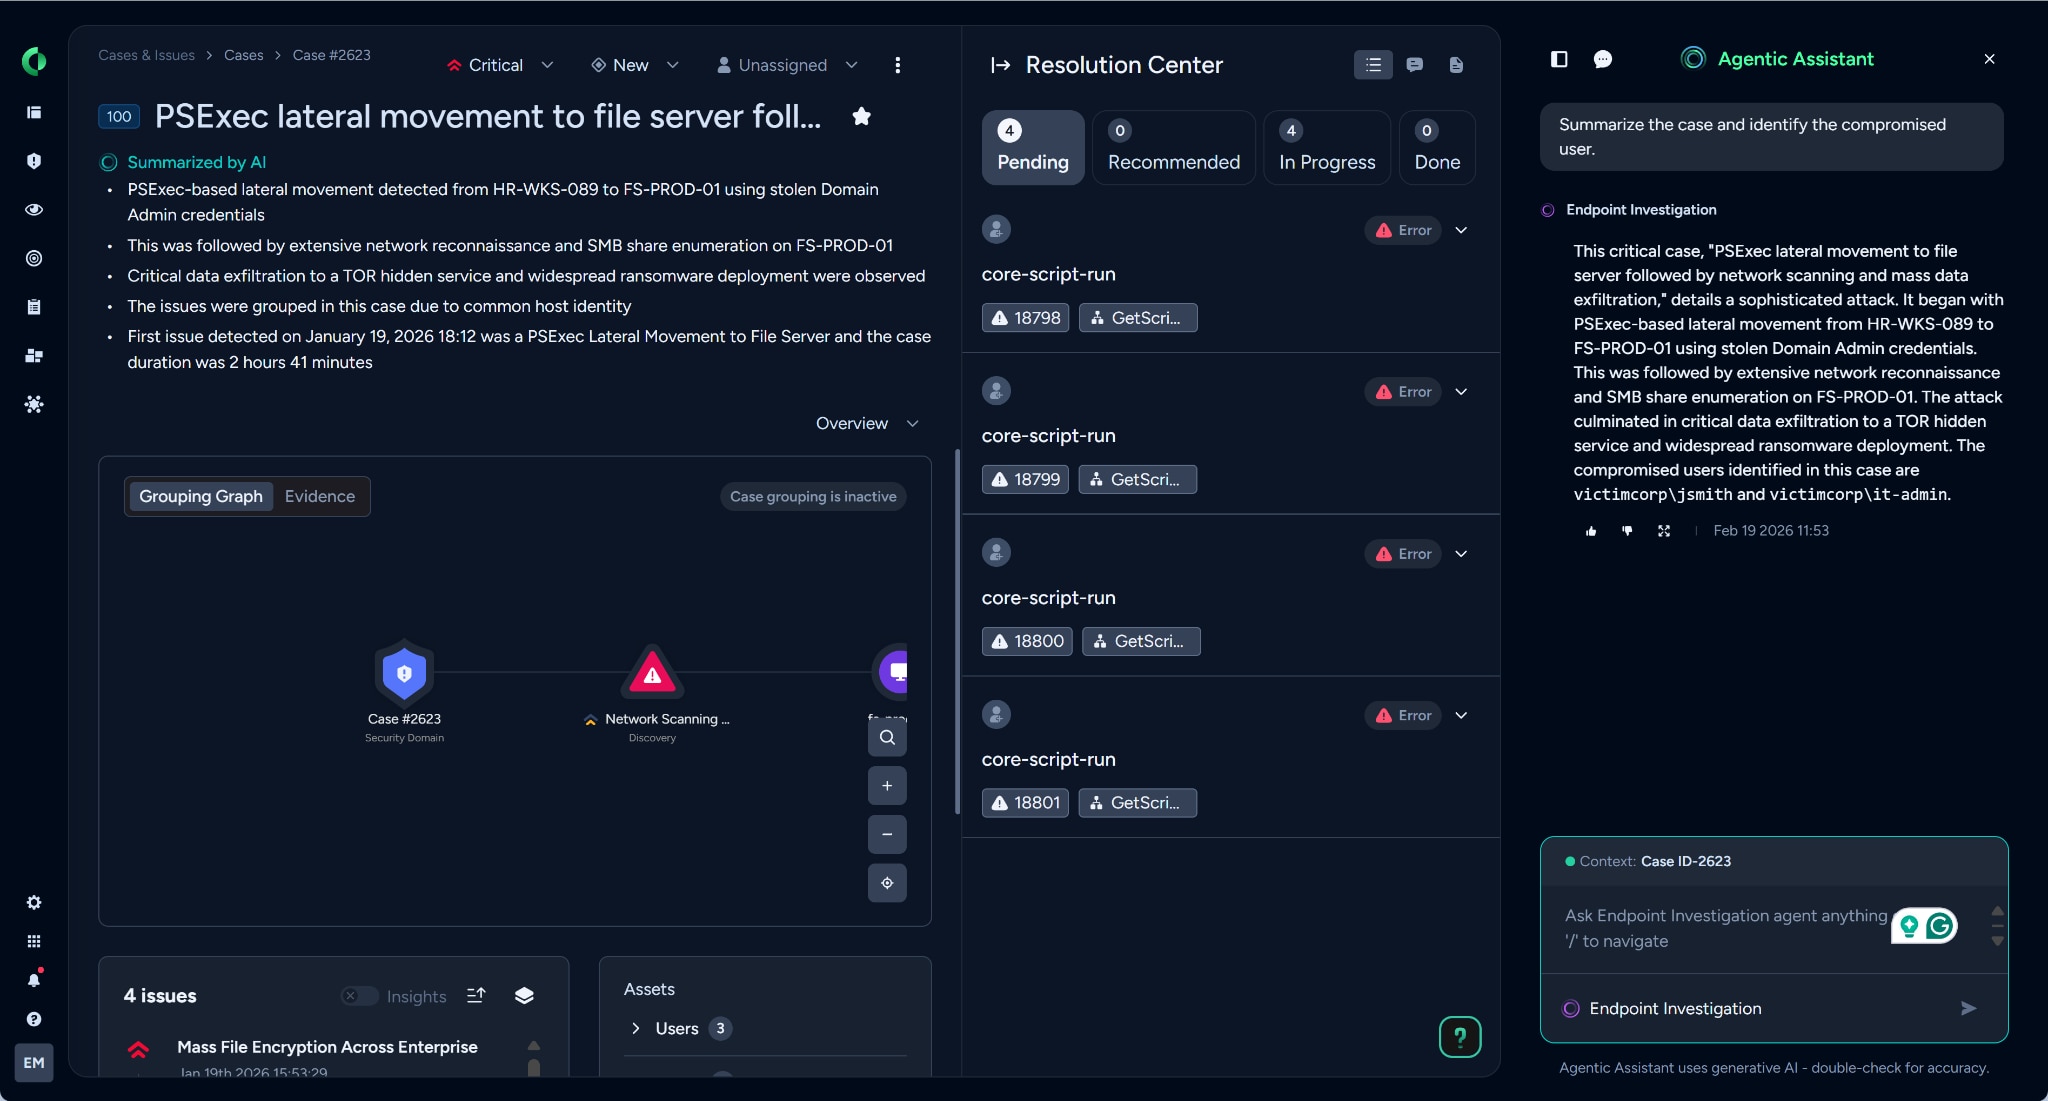
Products should correlate authentication, network, and execution activity across systems to identify movement that may appear less suspicious when each endpoint is examined separately. Indicators can include one account suddenly accessing many machines, remote processes appearing across multiple endpoints, or unusual use of administrative shares. Detecting lateral movement early can limit the number of systems an attacker reaches before encryption begins.
Ransomware frequently attempts to:
Attackers may also delete logs or change monitoring settings to reduce visibility before deploying the ransomware payload. Protection products should monitor their own configuration and other security controls for unauthorized changes. Tamper protection can prevent users and processes without appropriate authorization from disabling critical defenses. Products should also generate high-priority alerts when security controls are modified unexpectedly, since defense evasion can indicate that an attacker is preparing for later stages of an intrusion.
Attackers may delete volume shadow copies, disable recovery features, erase backup catalogs, or compromise connected backup infrastructure before encryption begins. Removing recovery options increases the operational impact of ransomware and makes restoring systems without external backups more difficult.
Products should:
Attempts to access or modify many backups at once can also provide an early warning signal. Immutable or isolated backups add another recovery layer because compromised administrator accounts or endpoints cannot easily alter them.
Many ransomware operations steal sensitive data before encrypting systems and then use the threat of disclosure as additional leverage. Attackers may:
Detection should cover unusual archive creation, large-scale file access, data staging, and unexpected outbound transfers to cloud storage or unfamiliar destinations. Network monitoring can help identify unusual transfer volumes or protocols, while endpoint telemetry can reveal which processes collected and prepared the data. Correlating exfiltration with credential abuse, lateral movement, and defense evasion provides stronger evidence of a broader ransomware operation.
Real-time behavioral detection identifies ransomware by monitoring what processes do rather than relying only on known malware signatures. Products should detect behaviors such as rapid file modification, mass encryption, unusual file renaming, shadow copy deletion, and attempts to access large numbers of files.
Behavioral detection is especially useful against new ransomware variants and customized payloads that signature-based tools may not recognize. Strong products correlate several suspicious events before taking action, helping distinguish ransomware from legitimate applications that perform high-volume file operations.
Application allowlisting restricts execution to approved applications, scripts, libraries, and other executable content. A Deny by Default approach blocks software unless it meets defined trust rules, reducing the opportunity for unknown ransomware payloads to run.
Products should provide flexible policies based on factors such as file hashes, publishers, certificates, paths, and application reputation. Administrators also need controlled exception workflows because overly restrictive policies can interfere with legitimate software updates, internal applications, and administrative tools.
Ransomware operators frequently use PowerShell, command shells, and scripting engines to download payloads, change configurations, or execute malware. Protection products should monitor script contents, command-line arguments, encoded commands, and suspicious relationships between processes.
Controls can restrict which users or applications are permitted to launch interpreters and block known dangerous execution patterns. Detailed command-line logging also gives security teams useful context when investigating an alert and determining which actions occurred before ransomware execution.
Credential theft detection identifies attempts to obtain passwords, hashes, authentication tokens, and other credentials from endpoints. Products should monitor access to sensitive processes and credential stores, including unusual interaction with LSASS and other authentication components.
Detection should cover behavioral techniques rather than only known credential-dumping utilities. The product should also correlate suspicious credential access with later authentication activity, helping security teams identify when stolen credentials are being used to access additional systems.
Automated endpoint isolation disconnects a suspected compromised device from most network resources while preserving communication with the security platform. This can prevent ransomware from spreading to shared storage, servers, and other endpoints.
Products should support both automatic isolation based on high-confidence detections and manual isolation initiated by security teams. Administrators should also be able to define exceptions for necessary management services and restore connectivity after the affected system has been investigated and remediated.
Ransomware protection products should be able to block malicious processes before they execute or terminate them when dangerous behavior is detected. Fast intervention is important because ransomware can encrypt large numbers of files within a short period.
Process controls should consider executable reputation, process ancestry, command-line arguments, code behavior, and interactions with other applications. Products should also terminate related child processes when appropriate so stopping one component does not leave another part of the ransomware chain running.
Monitoring file and registry activity helps identify the system changes associated with ransomware execution, persistence, and defense evasion. Relevant behaviors include rapid file modifications, extension changes, deletion of recovery data, creation of persistence entries, and modifications to security settings.
Products should record which process and user account performed each important change. This context helps distinguish malicious activity from normal software operations and provides useful evidence during incident investigation. Some products can also use this information to reverse selected changes or support file recovery.
Anti-tampering controls prevent attackers from disabling or modifying the security product after gaining access to an endpoint. They can protect security services, processes, configuration files, registry settings, policies, and local agents from unauthorized changes.
Effective tamper protection should continue operating when an attacker obtains elevated privileges. Products should detect attempts to stop services, uninstall agents, change exclusions, or weaken security policies and send alerts when these actions occur. Centralized controls can further prevent compromised local administrator accounts from changing protection settings.
How we selected these products: We shortlisted ransomware protection products based on application control and Deny by Default enforcement, behavioral and script-based detection, credential theft and lateral movement detection, automated endpoint isolation, and anti-tampering capabilities.
Best for: Deny by Default application control across IT, OT and legacy systems
Strengths: Granular allowlisting, LOLBin blocklisting, VirusTotal intelligence
Things to consider: Policy upkeep where apps update often; frequent agent releases
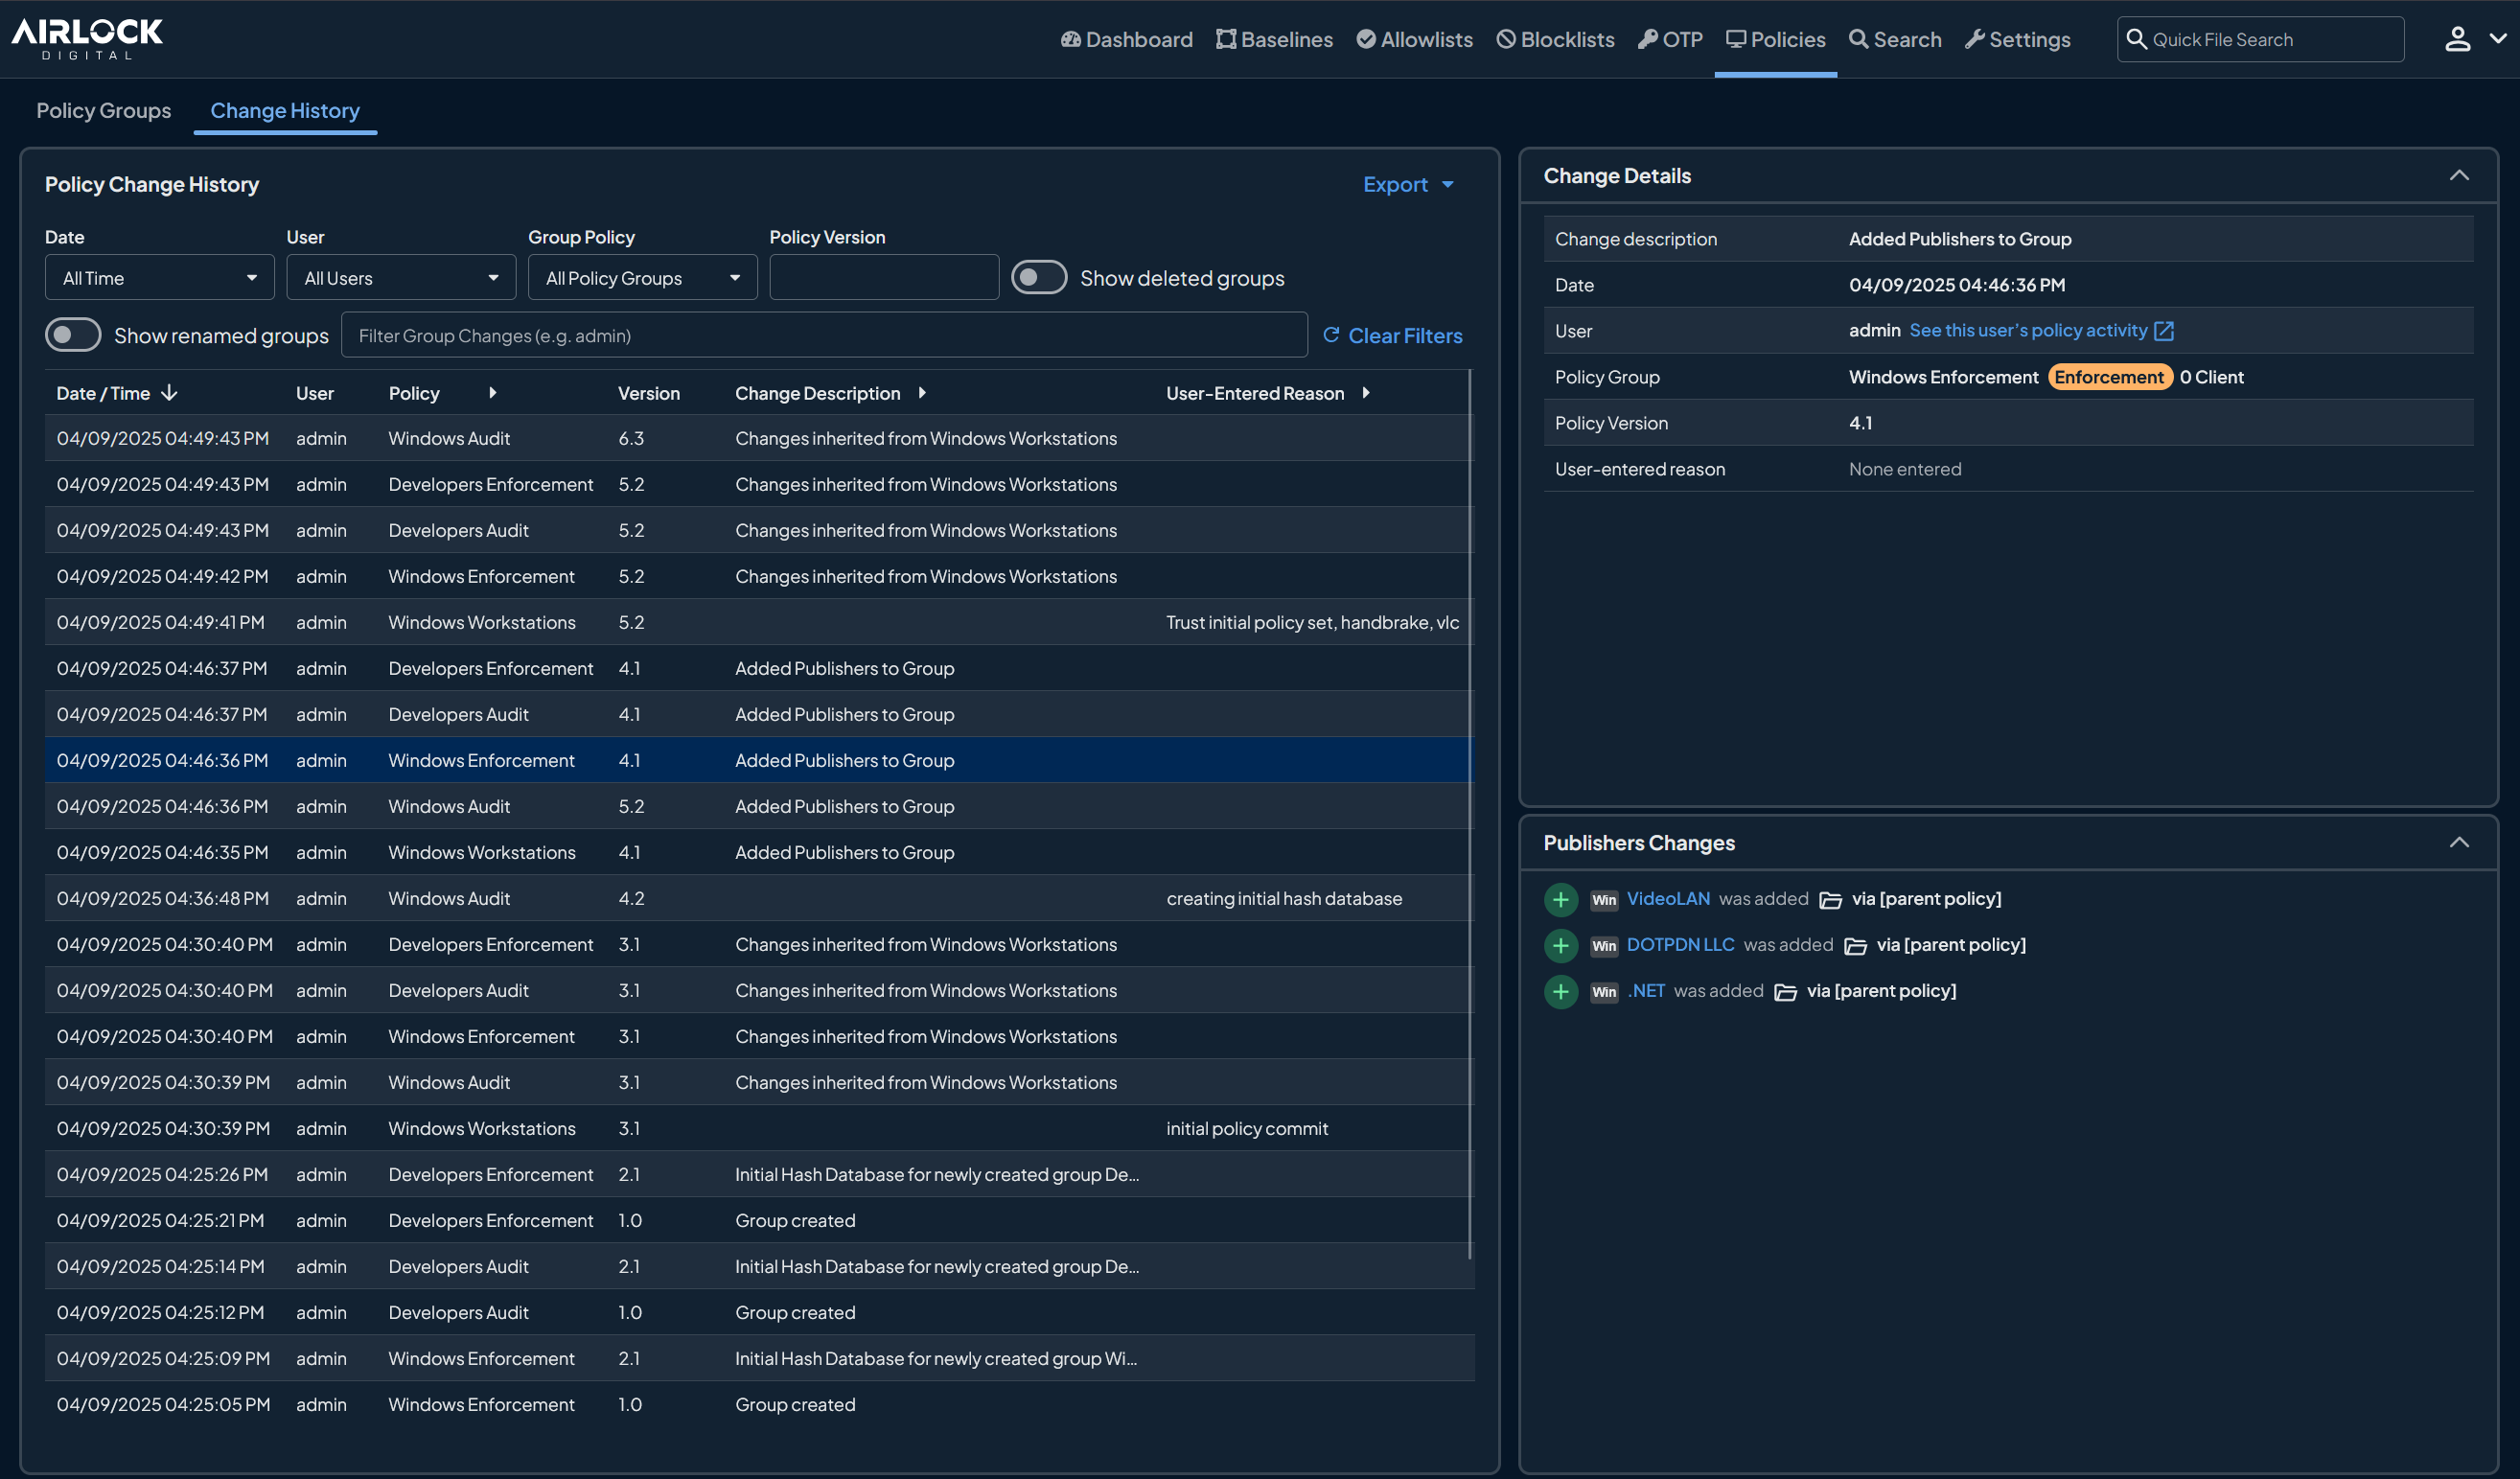
Airlock Digital is an application control solution that enforces a Deny by Default model on endpoints, so only trusted applications, scripts, libraries and processes are permitted to execute and everything else is blocked. Trust is defined at the file, path, publisher or parent process level. The platform also blocklists unauthorized use of trusted binaries such as PowerShell and WMI to prevent Living off the Land attacks.
It runs on current and legacy versions of Windows, macOS and Linux, extends to OT and air-gapped environments through an offline mode, and integrates with VirusTotal, CrowdStrike, Jamf and SIEM tools. Exception handling uses rule-based overrides and One-Time Passwords (OTPs) so administrators can grant temporary execution without weakening the overall policy.
Key features include:
Limitations (as reported by users on PeerSpot):
Source: Airlock Digital
Best for: Zero Trust endpoint platform combining allowlisting and Ringfencing
Strengths: Ringfencing app containment, dynamic ACLs, device isolation
Things to consider: Steep learning curve; app updates need re-approval
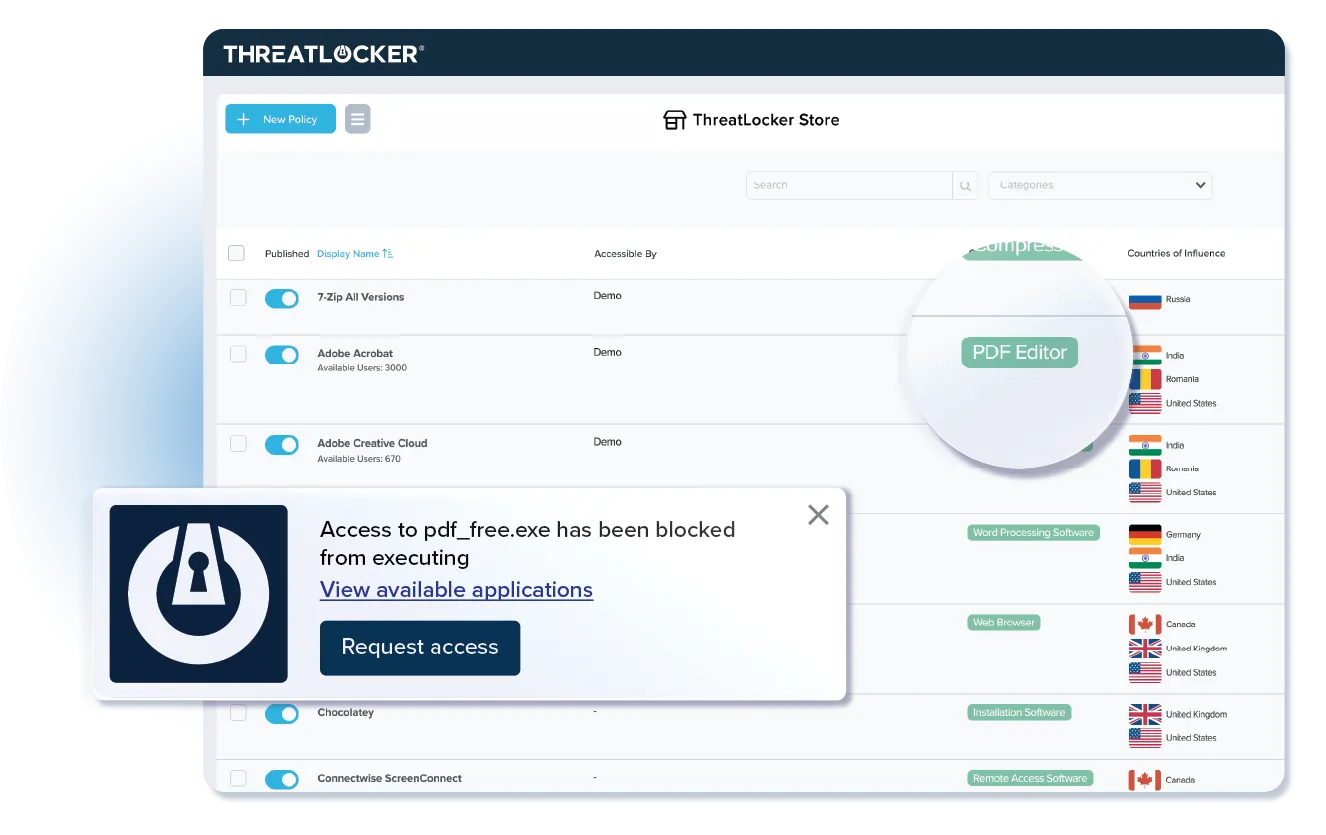
ThreatLocker is a Zero Trust endpoint protection platform that denies execution of unknown binaries, scripts and libraries by default and then restricts what approved applications are allowed to do. Its Ringfencing capability defines how applications interact with each other and with files, the registry and the network, so that Word cannot spawn PowerShell and PowerShell cannot open outbound internet connections.
The platform extends the same Deny by Default model to network and cloud access. Dynamic ACLs restrict RDP, SMB, WinRM and SSH to approved source devices, cloud access is refused when a request does not come from a trusted device, and EDR detection can isolate a compromised endpoint. Additional modules cover privileged access, storage control, patching and web content.
Key features include:
Limitations (as reported by users on G2):
Source: ThreatLocker
Best for: Locking down servers, fixed-function and EOL systems
Strengths: Positive security model with FIM, memory and registry protection
Things to consider: Allowlist upkeep at scale; vendor engagement since acquisition
Carbon Black App Control, now part of Broadcom, applies a positive security model in which unknown software is untrusted by default and must be explicitly approved before it can execute. It combines application allowlisting and denylisting with file integrity monitoring, device control, memory protection and registry protection, and can be deployed on-premises, in AWS, Azure or hosted private clouds.
The product supports Windows including XP, Server, Embedded/POS and ARM64, macOS, and RHEL and Oracle Linux, and is used to lock down air-gapped systems, fixed-function devices such as ATMs and POS terminals, and servers on end-of-life operating systems. Rather than maintaining static hash lists, it approves software through trusted directories, cloud reputation, trusted publishers and custom rules.
Key features include:
Limitations (as reported by users on Gartner Peer Insights):
Source: Carbon Black
Best for: AI-native EPP and EDR with managed threat hunting
Strengths: Indicators of attack, single lightweight sensor, OverWatch hunting
Things to consider: Modular licensing costs; console and query learning curve
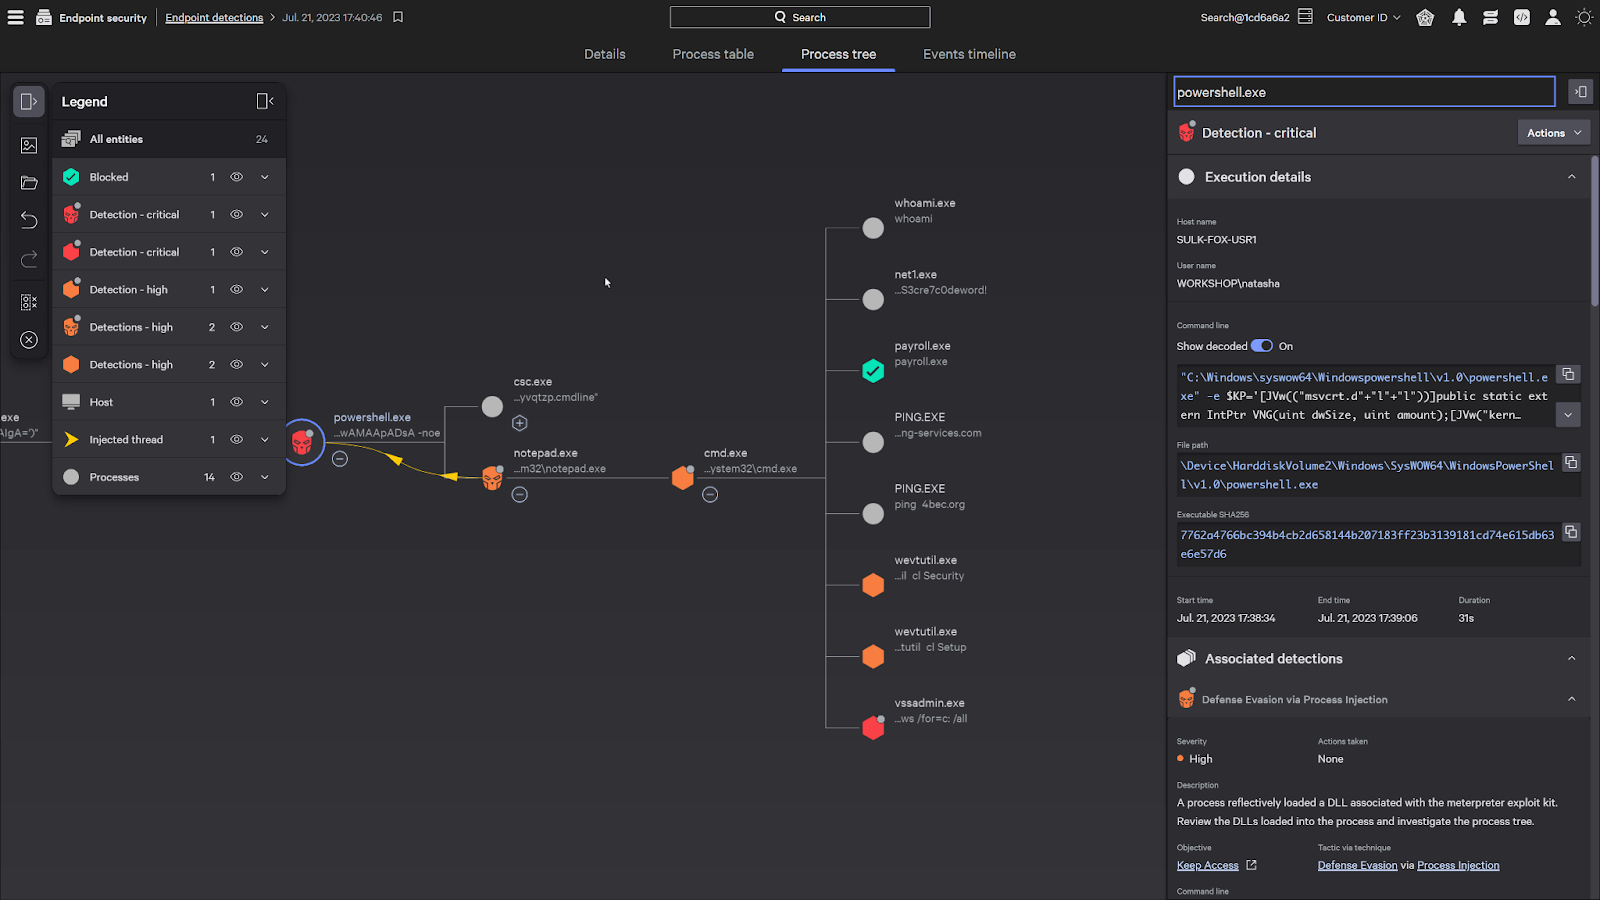
CrowdStrike Falcon delivers endpoint protection and EDR from a single lightweight sensor on the cloud-native Falcon platform. It combines on-sensor AI, adversary intelligence and indicators of attack to block known and unknown ransomware, malware-free intrusions and LIving off the Land techniques across Windows, macOS and Linux.
The platform continuously monitors endpoint behavior and correlates it with identity, cloud and third-party data in Falcon Next-Gen SIEM. OverWatch threat hunters monitor activity around the clock, and CrowdStrike also runs tabletop, red team/blue team and adversary emulation exercises to test ransomware defenses. It recorded 100% protection in the SE Labs EDR Ransomware Test for four consecutive years.
Key features include:
Limitations (as reported by users on G2):
Source: CrowdStrike
Best for: Autonomous EPP and EDR with 1-click ransomware rollback
Strengths: On-agent behavioral AI, Storyline correlation, rollback
Things to consider: Exclusion tuning at scale; query and console learning curve
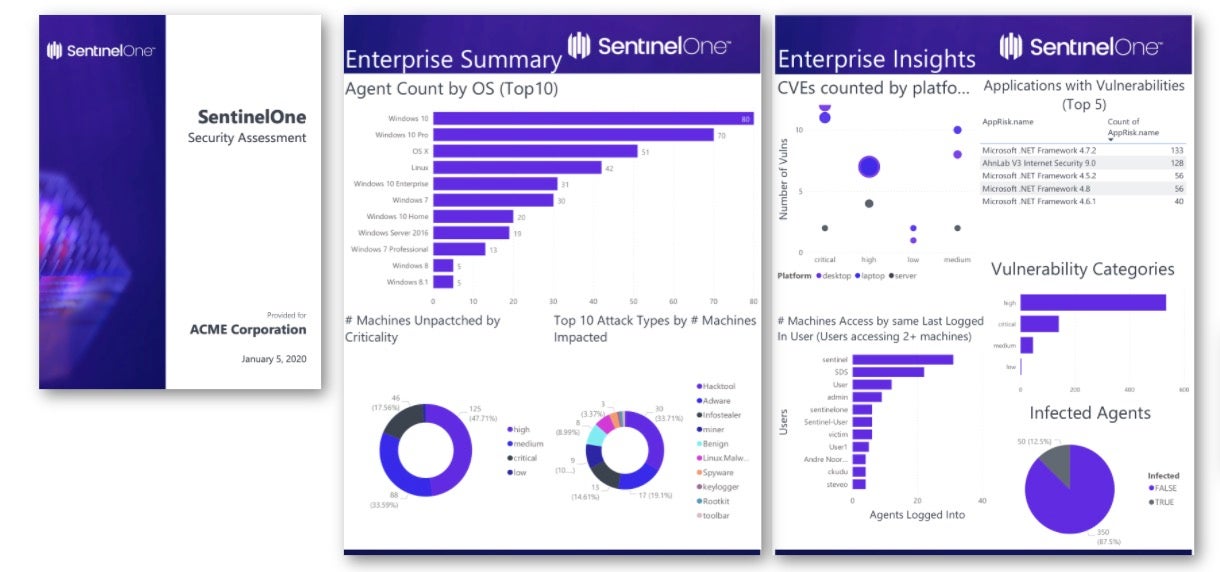
SentinelOne Singularity Endpoint unifies endpoint protection, EDR and identity correlation in one agent that runs behavioral AI locally, so detection and containment continue when a device is offline. The behavioral model identifies ransomware, zero-day exploits, supply chain attacks and fileless malware by what processes and users do rather than by signatures.
When a threat is detected, automated or 1-click response contains it and rollback reverses ransomware and unauthorized changes without reimaging. Storyline correlates every related process, file, network and identity event into one attack narrative with up to 365 days of retention, and Purple AI supports natural-language investigation. The agent deploys across SaaS, on-premises, hybrid and air-gapped environments.
Key features include:
Limitations (as reported by users on G2):
Source: SentinelOne
Best for: Multiplatform EDR integrated with the Microsoft security stack
Strengths: Automatic attack disruption, global threat intel, Defender XDR
Things to consider: Multiple portals; complex licensing; non-Windows parity
Microsoft Defender for Endpoint is a cloud-native endpoint security platform that delivers next-generation antivirus, EDR, mobile threat protection and advanced hunting across Windows, macOS, Linux, Android, iOS and IoT devices. It sits at the core of Microsoft Defender XDR, which correlates endpoint alerts with identity, email, SaaS and cloud signals.
Automatic attack disruption blocks lateral movement and remote encryption across devices in a decentralized way when a ransomware campaign is detected, with Microsoft reporting a three-minute average time to disrupt and 35,000 incidents disrupted per month. Threat intelligence draws on 84 trillion daily signals, and security settings can be managed from the Defender portal or mirrored in Intune.
Key features include:
Limitations (as reported by users on G2):
Source: Microsoft
Best for: Prevention-first endpoint protection with default-on mitigations
Strengths: CryptoGuard rollback, 60+ exploit mitigations, Adaptive Attack Protection
Things to consider: Resource use during scans; console navigation and reporting
Sophos Endpoint (Intercept X) is a unified endpoint protection and EDR agent for Windows, macOS and Linux that blocks the techniques attackers use rather than individual exploits or malware variants. More than 60 exploit mitigations are enabled by default on every running process without per-application tuning, alongside deep learning pre-execution detection and behavioral analysis.
CryptoGuard monitors file contents for malicious encryption, blocks the offending process whether it runs locally or on a compromised network device, and reverts encrypted files. Adaptive Attack Protection switches to more aggressive defenses when an active attacker is detected, and Synchronized Security shares telemetry with Sophos firewall, identity and email controls through Sophos Fusion.
Key features include:
Limitations (as reported by users on G2):
Source: Sophos
Best for: XDR combining endpoint, network, cloud and identity data
Strengths: Technique-based prevention modules, root-cause analysis, AgentiX
Things to consider: Learning curve for console and XQL; licensing complexity
Cortex XDR from Palo Alto Networks connects data from endpoint, network, cloud, identity and email sources and applies AI to detect and prioritize attacks that span multiple vectors. Its endpoint agent includes prevention modules built for individual techniques, from zero-day exploits to fileless malware and hijacking of legitimate processes.
When an alert fires, the platform uncovers the execution path and root cause, and native automation can disrupt the attack within minutes. The Cortex AgentiX Assistant adds AI agents that investigate and respond, and the same agent extends to NG-SIEM, endpoint DLP, exposure management and cloud security on the Cortex platform. Unit 42 provides MDR, managed threat hunting and incident response inside the tenant.
Key features include:
Limitations (based on publicly available sources):
Source: Palo Alto Networks
Advanced ransomware protection requires controls that can interrupt the attack chain before widespread encryption occurs. Organizations should evaluate products based on their ability to prevent unauthorized execution, detect script and LOLBin abuse, identify credential theft and privilege escalation, contain lateral movement, resist security tool tampering, and automatically isolate compromised endpoints. Effective protection should also combine behavioral detection with detailed investigation telemetry and resilient recovery measures to address both ransomware encryption and double-extortion attacks.